Customizing PrivX Carrier Browser
PrivX Carrier runs web browsers in containers to provide access to web targets. You can configure Carrier settings, customize browser features, restrict access to websites, and route web traffic through third-party proxies. Container reuse, memory requirements, and load balancing also affect how you configure and manage your deployment.
Configuring PrivX Carrier
To configure PrivX Carrier:
-
On each PrivX Carrier host, edit
/opt/privx/etc/carrier-config.tomlto configure browser container images, file-transfer settings, proxy ports, container networking, certificate trust, or connection timeouts as needed. -
Restart the PrivX Carrier service to apply the changes:
systemctl restart privx-carrier
To configure browser features, such as navigation controls and developer tools, use the PrivX Web UI as described below.
Customizing Web Browser Features
Configure browser features separately for each Web service in the PrivX Web UI:
-
Go to Administration → Hosts and edit the target host.
-
Under Services → Additional Settings for the Web service, enable or disable the following options:
Option Description Kiosk Mode Enable browser kiosk mode. Enable DevTools Allow users to open browser developer tools. Enable Urlbar Display the browser URL bar. Supported only in Firefox. Enable Navibar Display the browser navigation bar. Supported only in Firefox. Enable Popups Allow browser popups. Enable Plugins Enable compatibility mode for websites that do not work correctly with the password manager, such as some remote management consoles. Supported only in Firefox. -
Save the host configuration.
Disabling Enable Urlbar or Enable Navibar does not prevent users from following links to other websites. To restrict website access, configure one or both of the following:
- Host settings: Define allowed domains for individual Web services.
- Web Proxy settings: Define website access rules, including rules for specific PrivX roles.
For additional deployment configuration and planning, review the sections on third-party proxies, container reuse, memory requirements, and load balancing.
Restricting Web Access
Configure access restrictions for individual Web services using host settings or define access rules in the PrivX Web Proxy configuration.
Restricting Web Access Using Host Settings
To restrict the domains that the containerized browser can access:
- Go to Administration → Hosts and edit the target host.
- Under Services, expand Additional Settings for the Web service.
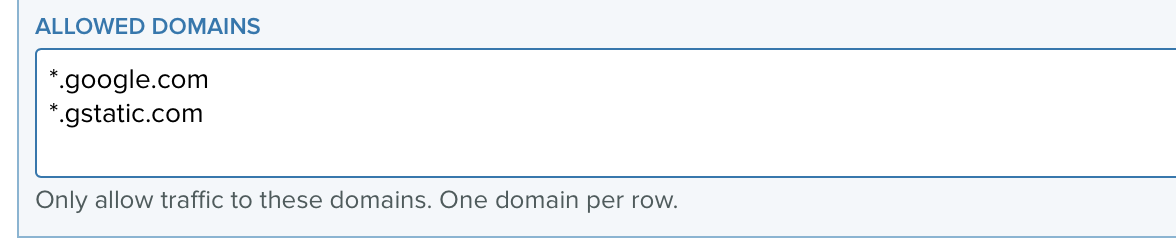
- In Allowed Domains, enter the allowed domains, one per line. Include all domains required by the target website, as many websites load content from multiple domains. If Allowed Domains is empty, this setting does not restrict access to any domains.
- Save the host configuration.
The setting applies only to the configured host. To restrict access based on PrivX roles, see Restricting Web Access Using Web Proxy Settings.
Restricting Web Access Using Web Proxy Settings
By default, PrivX Web Proxy allows connections to all websites. PrivX 29 and later do not use Squid to proxy web traffic.
To restrict access, edit /opt/privx/etc/privx-web-proxy.toml on the PrivX Web Proxy host.
You can define access rules for specific PrivX roles. These rules restrict access both when users enter URLs directly and when they follow links on web targets.
The following examples illustrate two different configurations:
-
Allowing Access for a Specific Role
To allow only members of the
privx-adminrole to accesshttps://www.example.com, apply the following configuration on all PrivX Web Proxy hosts:# Whitelisted urls. Traffic to these domains is always allowed. Wildcards are allowed, for example ['https://*.gmail.com','https://*.gstatic.com']# Use [""] to disable.# Default is to allow all traffic: ["*"]whitelisted_global_urls = ["",]# Role whitelisted urls. Traffic to these domains is always allowed for the defined roles. Wildcards are allowed.# Example:# whitelisted_role_urls = [# "privx-admin=https://*.gmail.com",# "privx-admin,developers=https://*.gstatic.com"# ]# Use [""] to disable.# Default: []whitelisted_role_urls = ["privx-admin=https://www.example.com"] -
Blocking Subdomains with Exceptions
To block subdomains of
examplesite1.comandexamplesite2.com, except for the explicitly allowed subdomain under each domain, use the following configuration:# Whitelisted urls. Traffic to these domains is always allowed. Wildcards are allowed, for example ['https://*.gmail.com','https://*.gstatic.com']# Use [""] to disable.# Default is to allow all traffic: ["*"]whitelisted_global_urls = ["https://whitelisted.examplesite1.com","https://whitelisted.examplesite2.com"]# Role whitelisted urls. Traffic to these domains is always allowed for the defined roles. Wildcards are allowed.# Example:# whitelisted_role_urls = [# "privx-admin=https://*.gmail.com",# "privx-admin,developers=https://*.gstatic.com"# ]# Use [""] to disable.# Default: []whitelisted_role_urls = [""]# Blacklisted urls. Traffic to these domains is blocked, unless explicitly allowed by whitelist. Wildcards are allowed.# Default is to block everything: ["*"]blacklisted_urls = ["https://*.examplesite1.com","https://*.examplesite2.com"]
Save the configuration file and restart the PrivX Web Proxy service to apply the changes:
# systemctl restart privx-web-proxy
If you need several access rules, consider configuring restrictions for individual hosts. For more information, see Restricting Web Access Using Host Settings.
Routing Traffic Through Third-Party Proxies
If the PrivX Web Proxy host cannot access the target network directly, configure a third-party proxy that supports HTTP CONNECT or SOCKS5.
In /opt/privx/etc/privx-web-proxy.toml, set proxy_url to the proxy URL. Use no_proxy to specify targets that PrivX Web Proxy connects to directly.
# Proxy URL specifies the http connect or socks proxy to use when connecting to target servers.
# Extender connections are never connected through the proxy.
# Supported proxy URL schemes:
#  "http": http connect protocol
#  "https": http connect protocol over a TLS connection
#  "socks5" / "socks5h": socks5 protocol
# If the value is empty the proxy URL and no proxy list are read from the ALL_PROXY and NO_PROXY environment
# variables.
# Example:
# proxy_url = "http://proxyuser:secret@proxy-server.io:8080"
proxy_url = ""

# No proxy defines target servers which should be connected directly bypassing the proxy. The target servers are specified
# as a comma separated list of IP addresses, CIDR ranges, domain patterns or hostnames.
# Example:
# no_proxy = "10.0.0.1,192.168.0.0/24,*.internal.privx.io,directly-connectable.privx.io"
no_proxy = ""
Save the configuration file and restart the PrivX Web Proxy service to apply the changes:
systemctl restart privx-web-proxy
Reusing Containers
PrivX Carrier supports Firefox and Chromium as browsers running in containers. By default, PrivX creates a separate container for each browsing session. Connections to different web targets or with different user accounts use separate containers.
If you connect to the same web target in another browser tab during the same PrivX login session, the new connection reuses the existing container and disconnects the connection in the previous tab. Only one tab can access the session at a time.
If you reload the page or your network connection is briefly interrupted, the browsing session continues using the same container.
If you close your native browser tab, you can reopen it within 60 seconds to reconnect to the same session.
If you close the browser running in the Carrier container, the session ends immediately, the container terminates, and its data is deleted.
Memory Requirements
Each browser session runs in a sandboxed and audited container. A Carrier host typically requires 250 MB to 1 GB of memory per active HTTPS session. A host with 64 GB of memory is expected to support approximately 50 concurrent web users. Resource-intensive tasks, such as watching videos, increase memory usage toward the upper end of this range, up to 1 GB per session.
PrivX Web Proxy forwards web traffic and requires less memory than PrivX Carrier. Each Carrier requires a dedicated Web Proxy to provide credentials for web logins.
You can install PrivX Carrier and PrivX Web Proxy on the same server. For security reasons, we recommend separate servers in production environments.
For more information about Carrier container features and customization, contact PrivX Enterprise Support.
Configuring Load Balancing
For load balancing traffic between Carrier instances, configure the Carrier and Web Proxy pairs with the same routing prefix in the PrivX Web UI. Use this routing prefix in the target host address.
To change the load-balancing algorithm, configure prefer_extender_or_carrier_with_least_connections in /opt/privx/etc/shared-config.toml on the PrivX server.
For security reasons, Carrier and Web Proxy credentials are bound to a single Carrier instance at a time. Each Carrier requires a separate configuration file.
Sharing credentials and running Carriers in an autoscaling group are not supported.